About
I help leaders make confident security decisions.
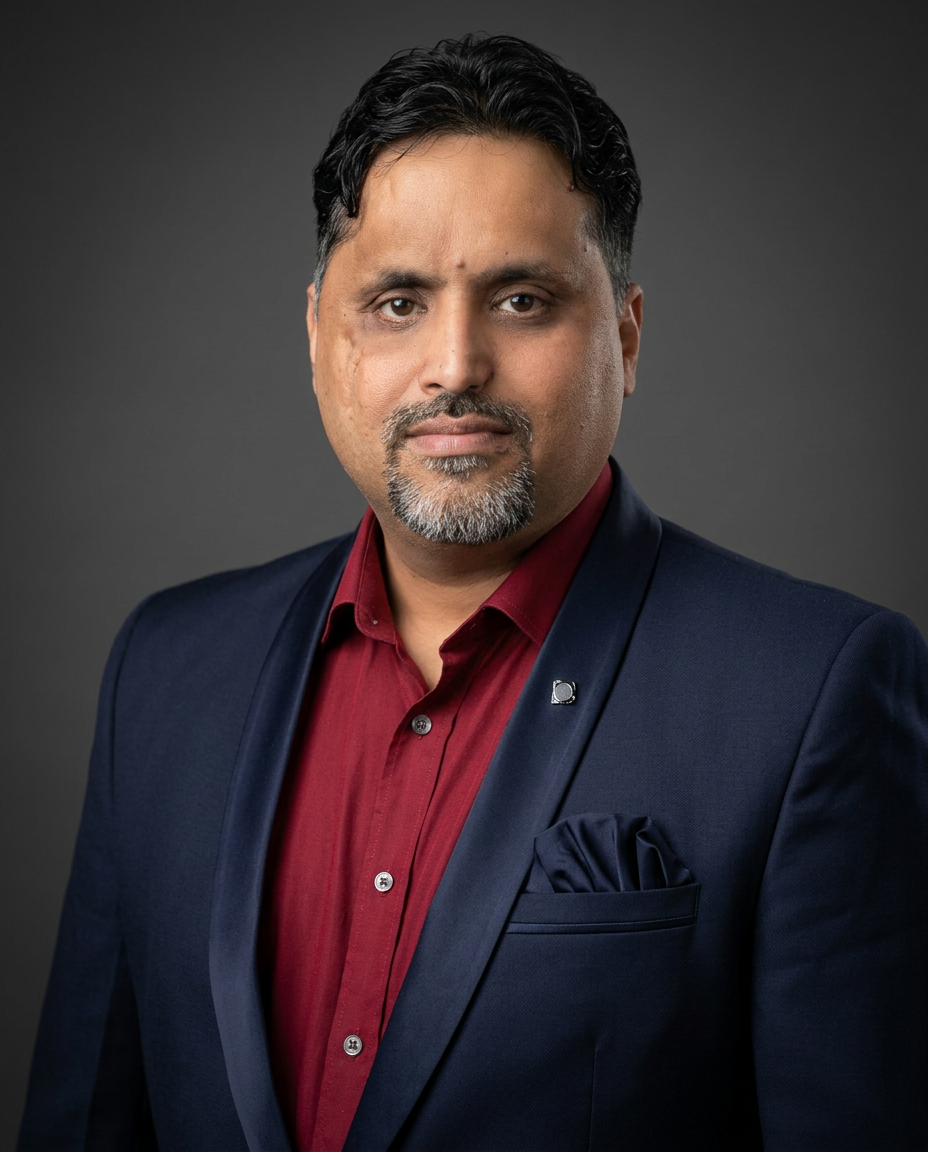
I'm Sagar Kamra. For nearly two decades I've worked across all stages of IT — implementation, operations, audit and security leadership. My superpower is translating dense control frameworks into decisions executives can sign off and engineers can ship.
Experience
2019 — Present
Fractional CTO · CISO-equivalent
Led the audit lifecycle for six consecutive years — zero non-conformities. Directed RFFR audits for 18 subcontractor organisations under a Commonwealth department programme. Sustained Essential Eight ML3 for five years and delivered a Zero Trust uplift. Acted as CISO-equivalent for a consulting practice and led a not-for-profit through a successful IRAP assessment.
Earlier career
Technology Manager · IT Security Specialist · Application Consultant
Owned full P&L for the IT department, delivered a 3-year digital strategy, automated quality and compliance via a low-code Quality Portal, integrated ISO 9001 and ISO 27001 governance and delivered 30% cost reduction.
Australia · India · Middle East
19+ years across all stages of IT
From application delivery and infrastructure to security leadership and GRC — engagements spanning government-regulated providers, consulting and not-for-profit sectors.
Domains
Sectors I've delivered in.
Nearly two decades of engagements across regulated industries, public sector and social impact.
Services
Beyond security — into transformation.
Three specialist engagements that bridge governance, operations and commercial outcomes.
I also build AuditPro — an Australian-sovereign compliance platform used across my ISO 27001, IRAP and Essential Eight engagements.
System Digitisation
Retire paper, spreadsheets and shared inboxes — at audit-grade quality.
Read about System DigitisationBusiness Process Automation
Remove manual bottlenecks. Build governed, auditable workflows.
Read about Business Process AutomationVendor & Supplier Renegotiation Engagement
Project-scoped renegotiation tied to transformation and renewal events.
Read about Vendor & Supplier Renegotiation EngagementCredentials & highlights
Receipts, not just résumés.
A snapshot of the frameworks, programmes and outcomes I've personally led. My hands-on technology and security leadership is supported by assessed lead-auditor training in ISO 27001:2022 and integrated management systems covering quality, environmental management and occupational health and safety.
Work with me- 01ISO 27001 Lead Implementer & Lead Auditor experience
- 02ISO 27001:2022 Lead Auditor — JLB Management Consultancy, October 2026
- 03Integrated Management System Lead Auditor (ISO 9001 · ISO 14001 · ISO 45001) — JLB Management Consultancy, August 2026
- 04Essential Eight Maturity Level 3 — 5 years sustained
- 05Zero Trust Network Architecture uplift delivered
- 06IRAP assessment leadership for a not-for-profit
- 07RFFR subcontractor governance experience
- 08Contributor to a Commonwealth GRC tool
Certifications
 Microsoft Certified Technology Specialist
 Microsoft Certified IT Professional (MCITP)
 ISO 27001:2022 Lead Auditor
 IMS Lead Auditor — ISO 9001 · 14001 · 45001
 ISO 27001 Lead Auditor (legacy)
 ITIL V3 Certified
 Certified ISO 27001 Lead Implementer
 Certified ISO 27001 Internal Auditor
 ISO/IEC 27001 Information Security Risk Manager
 Certified in Cybersecurity (CC)
 Certified Information Security Lead Professional
 ISO/IEC 27001 Information Security Executive