Zero
Non-conformities across 6 ISO 27001 audits
Designed and led the ISMS through six consecutive surveillance and recertification cycles without a single non-conformity.
Sydney · Independent Specialist · Est. 2006
Fractional CTO advisory paired with independent cyber and digital specialist services — for government providers, not-for-profits and mid-market organisations who need technology strategy, defensible governance and audit-ready controls without retaining a Big Four engagement.
By the numbers
19+
Years in IT & Security
6
Consecutive ISO 27001 audits, zero non-conformities
18
Subcontractor RFFR assessments led
ML3
Essential Eight, 5 years sustained
Specialist services
Fractional CTO accountability — technology strategy, architecture and delivery oversight without the full-time cost.
Explore CTO-as-a-ServiceExecutive-grade security leadership on a fractional retainer — risk, strategy, board and regulator reporting.
Explore CISO-as-a-ServiceDelivery-focused vCISO — ISMS ownership, control execution and audit prep on a defined scope.
Explore Virtual CISO (vCISO)Implementation, gap assessment and certification readiness designed to pass external audit and operate sustainably.
Explore ISO 27001 Advisory & Audit ReadinessACSC ISM preparation, System Security Plan authoring and assessor liaison — end to end.
Explore IRAP Readiness & Assessment SupportIndependent maturity assessments and pragmatic roadmaps to ML2 / ML3 — no over-engineering, no vendor agenda.
Explore Essential Eight AssessmentsFrom Essential Eight to ASD Essentials: one baseline, one evidence base, a transition plan sequenced by Priority Phase.
Explore Essentials Assessment & TransitionWhy clients engage me
CEOs, CIOs, boards and risk committees engage me for clarity, accountability and audit-ready outcomes — without the bloat of a tier-one consultancy.
Technology strategy, architecture and security governance from a single accountable operator — no handoffs between a CTO advisor, vCISO and integrator.
No product quotas, no vendor incentives. Advice is calibrated to your risk, budget and roadmap — not a partner programme.
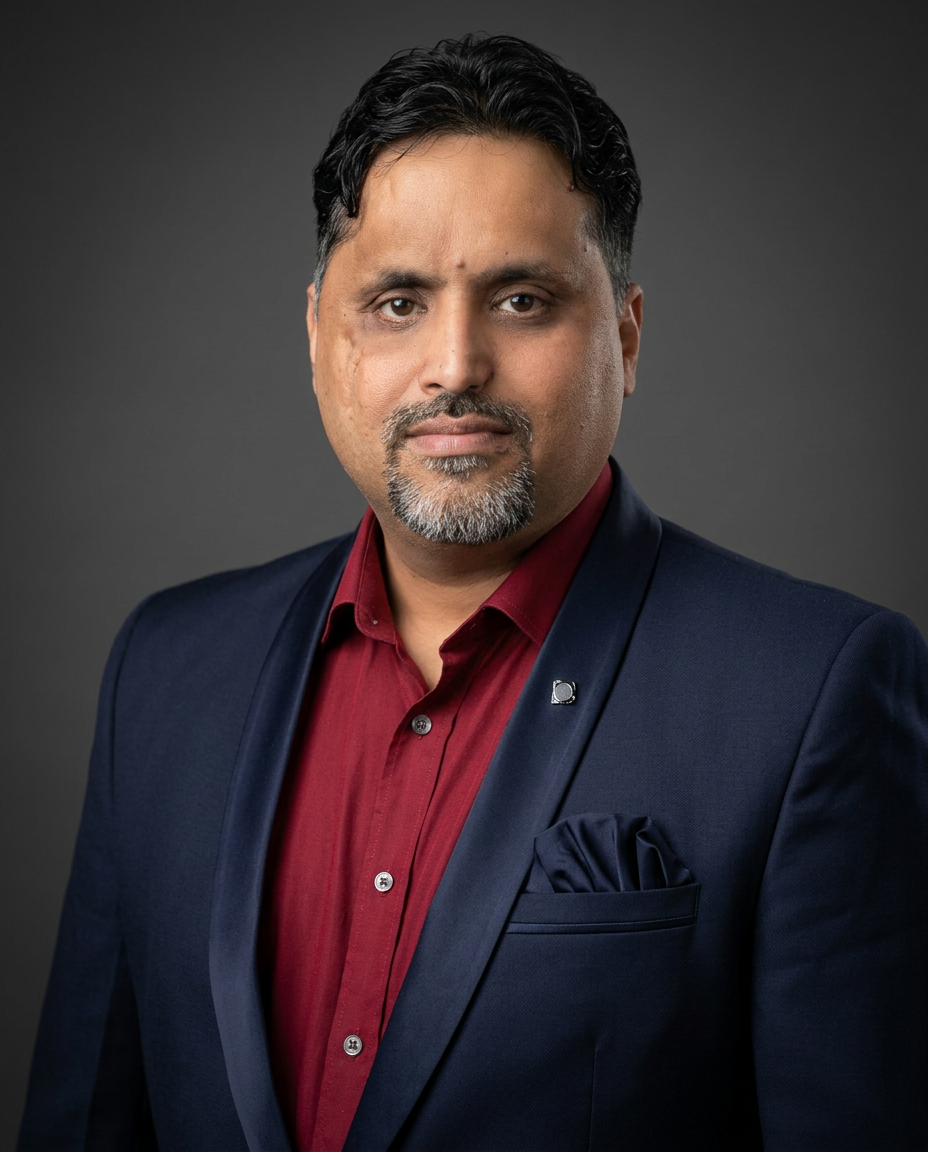
I've owned the program — CTO, CISO and delivery leadership across hybrid Microsoft, Azure and SaaS estates — not just audited it.
Six consecutive ISO 27001 surveillance and recertification audits delivered with zero non-conformities.
Frameworks & expertise
Deep working knowledge of cloud architecture, Microsoft platforms, and ACSC, ISO and NIST control sets — translated into pragmatic, auditable technology programs for organisations operating under government and regulator scrutiny.
Selected engagements
Zero
Designed and led the ISMS through six consecutive surveillance and recertification cycles without a single non-conformity.
18
Led Right Fit For Risk readiness for a government provider and its subcontractor network — uplifted to government expectations.
ML3
Took an organisation from baseline to Maturity Level 3 and held it through hybrid Microsoft and SaaS environments.
Product · AuditPro
I don't just advise — I ship the Australian-sovereign platform that IRAP assessors, implementers and certification bodies actually use.
Explore AuditProSovereign
Hosted only in ap-southeast-2. CLOUD Act exclusion attestation.
PSPF-aware
Every artefact classified UNOFFICIAL → TOP SECRET. Flows blocked at platform level.
IRAP-native
SSP, SRMP, SAR generation + ASD-format exports. Not translated from a US GRC schema.
Assessor ↔ Implementer
Zero re-keying between the two sides. Evidence submitted once, referenced everywhere.
Case studies
Commonwealth supply chain · Government-contracted prime
Led Right Fit For Risk (RFFR) readiness for a Commonwealth-contracted prime and 18 subcontractors in its supply chain — from fragmented baselines to a common ACSC ISM and Essential Eight ML2 posture across the network.
Read case studyRegulated services · Mid-market
Designed and led an ISO 27001 Information Security Management System through six consecutive surveillance and recertification audits — every cycle closed with zero non-conformities.
Read case studyNot-for-profit · Commonwealth-adjacent
Led a not-for-profit through an IRAP assessment against the ACSC ISM — from ad-hoc controls to a defensible System Security Plan and a clean assessor engagement.
Read case studyLatest writing
The Essential Eight is growing up. What the new framework means, and the five moves to make in your first week.
Read the summary Week 2 · Deep diveCohort-by-cohort adoption, integrating your Maturity Level 2 uplift with the Essentials transition, and the three-year cost journey.
Read the deep dive Standalone · First 30 daysA new framework doesn't mean starting again. How to use Essentials, keep existing commitments, and make the first 30 days count.
Read the 30-day guideCertifications
How we work together
A confidential conversation to understand context, drivers, regulators and the outcome that matters.
Structured review of current state against the relevant framework — ISO 27001, Essential Eight, RFFR or ISM.
A prioritised, costed plan calibrated to your risk appetite, change capacity and certification timeline.
Hands-on specialist support through implementation, audit and continuous improvement.
Client perspectives
Names withheld · scroll to read
Identities of clients and organisations withheld. Full references available on request under NDA.
Begin the conversation
A 30-minute Fractional CTO call — no pitch, no scripted discovery. Just a candid conversation about the outcome you need and whether I'm the right person to help you get there.
All initial conversations are confidential. Engagements operate under NDA where required.